Lotus365 ID and Password Security: Building a Safer Account Routine
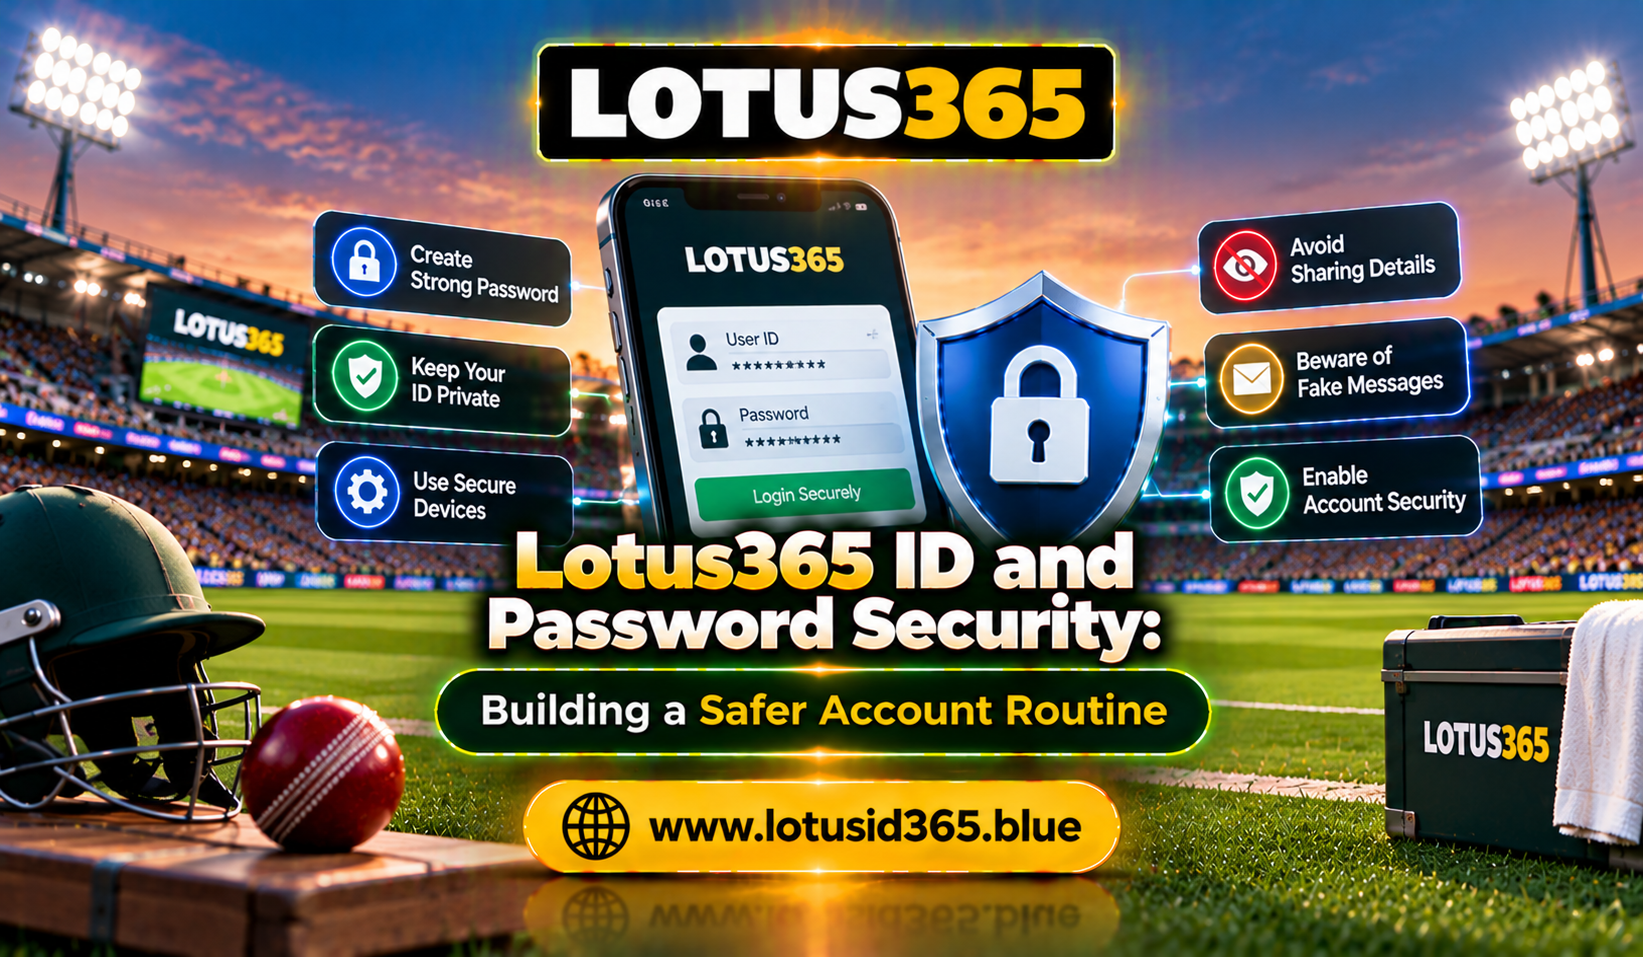
Protecting online account credentials is an important part of maintaining privacy and reducing the risk of unauthorised access. Weak passwords, reused credentials, suspicious login links, and careless sharing of personal information can create avoidable security problems. Understanding Lotus365 includes recognising the importance of responsible credential management. Regardless of which online service a person uses, account security should begin with strong passwords, careful website verification, and a clear understanding of how recovery procedures work.
Users accessing services through a Lotus365 Login should also consider device security, software permissions, and the source of the website or application. A mobile device that is shared with other people or contains outdated software may introduce additional risks. Good security habits do not require advanced technical knowledge. Consistent practices, such as using unique passwords and avoiding suspicious links, can make everyday account management safer and easier to maintain.
Get Lotus365 ID: https://lotusid365.blue/
Why Password Security Matters
A password is often the first barrier protecting an online account. If it is easy to guess, reused across multiple services, or shared with another person, an unauthorized individual may have an easier opportunity to gain access.
Password security matters because accounts may contain contact details, account preferences, recovery information, and other private data. A compromised email account can be especially concerning because it may be used to reset passwords for other services.
Even a password that seems strong can become vulnerable if it is entered on a fraudulent website or stored in an insecure location. Therefore, account protection requires more than creating a complicated password once. It involves managing credentials carefully throughout the account's lifetime.
Create a Strong and Unique Password
A strong password should be difficult for another person to guess. Avoid using obvious personal information, including birthdays, phone numbers, names, or familiar sequences such as consecutive numbers.
Longer passwords generally provide better protection when they are unpredictable. A passphrase made from several unrelated words can be easier to remember while remaining difficult to guess, provided it is sufficiently long and not a common phrase.
Most importantly, use a different password for every important account. Reusing the same password creates a chain of risk: if one website experiences a data breach, criminals may try the exposed credentials on other services.
A reputable password manager can help generate and store unique passwords. Protect the password manager itself with a strong master password and any additional authentication options it supports.
Keep Passwords Private
Never share your password with an unfamiliar person who claims to provide technical assistance. A request for a password through chat, email, or social media should be treated with caution.
Avoid writing credentials on visible notes, leaving them in public places, or saving them in unprotected documents. If you need to keep a written backup, store it somewhere secure and inaccessible to other people.
Be careful when entering a password in front of others. Someone nearby may see your screen or observe your typing, particularly in public settings.
If another person needs access to a device, use appropriate device-level sharing controls rather than disclosing your private account credentials. Sharing passwords can make it difficult to determine who accessed an account if something goes wrong.
Verify the Website Before Signing In
Even a strong password cannot protect an account if it is entered into a fraudulent website.
Before signing in, inspect the complete domain name. Look for misspellings, unexpected extra words, unfamiliar domain endings, and redirects to unrelated websites. Do not rely solely on logos, colours, or a professional-looking design.
Avoid following sign-in links from unexpected messages. Instead, navigate to a website through a trusted source that you have independently verified.
An HTTPS connection helps protect data while it travels between your browser and a website, but it does not prove that the website itself is trustworthy. Fraudulent websites can also use encrypted connections.
If the domain cannot be verified, do not enter your password or personal information. Taking a moment to confirm the address is safer than trying to resolve a problem after credentials have been exposed.
Use Additional Authentication Protection
Some online services offer an extra verification step in addition to a password. This may involve an authentication application, a security key, or a one-time code.
When available, additional authentication can make unauthorised access more difficult, particularly when a password has been exposed. Choose the strongest practical option supported by the service.
Keep recovery codes in a secure location and never send them to another person. Treat one-time codes as private authentication credentials, even when someone claims to be a support representative.
Remember that additional authentication is not a reason to ignore suspicious sign-in requests. If you receive an unexpected approval notification or code, do not approve an activity you did not initiate. Change your password through the verified website if you suspect someone else is attempting to access the account.
Protect Your Phone and Computer
Account security also depends on the device used to access a service. Outdated operating systems and browsers may contain security weaknesses that attackers can exploit.
Install updates through the device's official update settings. Use a screen lock, keep security protections enabled, and avoid installing unknown applications or browser extensions.
For Android devices, be particularly careful with APK files obtained from unfamiliar websites. A file's name or icon does not prove its authenticity. Review the source and requested permissions before installing software.
On iPhones and computers, avoid configuration profiles, downloads, or remote-access tools supplied by unknown contacts. An unsolicited offer to fix an account problem does not justify granting someone control over your device.
If a device is shared, use separate user profiles when possible and avoid saving passwords in a browser that other people can access.
Be Careful on Public and Shared Networks
Public Wi-Fi networks can be convenient, but users should be cautious when accessing accounts over networks they do not control.
Prefer a trusted, password-protected network when entering sensitive information. Avoid connecting to unfamiliar Wi-Fi hotspots simply because their names resemble those of legitimate businesses.
HTTPS protects information in transit, but users still need to verify the website and watch for deceptive login pages. A fraudulent hotspot or phishing page may attempt to collect information without needing to defeat encryption.
When using a shared computer, do not select options that save your password. Sign out when finished, close the browser, and check that the next user cannot access your account.
Private browsing can reduce the storage of certain local browsing information, but it does not make a device completely secure or hide all activity from networks and websites.
Change a Password When Necessary
Changing a password is useful when there is a genuine reason to believe that it may have been exposed. Examples include receiving a credible breach notification, entering credentials on a suspected fake page, or noticing unfamiliar account activity.
Use the verified website's password-change or recovery process. Choose a new password that has not been used for another account.
If you suspect unauthorised access, review available account sessions and sign out unfamiliar devices where the service permits it. Secure the associated email account as well, since email access may be used for password recovery.
Avoid changing passwords through links supplied in suspicious messages. Open the legitimate website independently and begin the process there.
If you cannot access the account, use the provider's official recovery instructions. Do not trust people who promise guaranteed recovery in exchange for your password, verification code, or an unverified payment.
Review Account Activity and Recovery Details
Regularly reviewing account settings can help identify problems before they become more serious.
Where available, check recent login activity, recognised devices, contact information, and security notifications. Investigate activity you do not recognise rather than assuming every notification is harmless.
Make sure the registered email address and phone number remain under your control. Outdated recovery details can make it harder to regain access when a password is forgotten or a security check is required.
If a service provides alerts for new devices or unusual sign-ins, consider enabling them. Respond to unexpected alerts through the verified website rather than using links in the notification.
The settings available will vary by provider. Do not assume that every service offers the same security controls or account activity information.
Build a Simple Security Routine
A useful security routine should be easy enough to follow consistently. Use unique passwords, keep software updated, verify website addresses, and protect recovery information.
When signing in, pause before entering credentials and check the domain. When receiving an unexpected verification message, confirm that you initiated the activity. When installing software, verify its source and review its permissions.
Avoid sharing sensitive information in public posts or support conversations. If you need technical help, describe the error and provide non-sensitive details rather than sending passwords or authentication codes.
These habits can reduce common risks without requiring users to become cybersecurity experts.
Frequently Asked Questions
1. How often should I change my password?
Change it promptly if you suspect exposure, receive a credible breach warning, or notice suspicious activity. Regular changes without a reason are less important than using a strong, unique password and changing it when necessary.
2. Is it safe to reuse one password across multiple accounts?
No. If one service is compromised, reused credentials may be tested against other services. Use a different password for every important account.
3. Should I share my OTP with support?
No. Keep one-time codes and recovery codes private. Enter them only into the legitimate verification process for an action you initiated.
4. Does HTTPS guarantee that a website is genuine?
No. HTTPS helps encrypt the connection, but fraudulent websites can also use it. Always inspect and verify the complete domain.
5. What should I do if I suspect my password has been stolen?
Change it through the verified website, secure any other accounts using the same password, review available login activity, and sign out unfamiliar sessions where possible. Also secure the associated email account.
6. Can a password manager improve account security?
A reputable password manager can generate and store unique passwords, reducing the need to reuse or memorise credentials. Protect it with a strong master password and any supported additional authentication.
Conclusion
Safer account management begins with strong, unique passwords and careful control of personal information. Verifying website addresses, protecting authentication codes, updating devices, and reviewing account activity can reduce common security risks.
No single measure guarantees complete protection, but consistent habits make accounts harder to compromise. Use verified access and recovery methods, avoid suspicious support messages, and never disclose confidential credentials to unknown individuals. A simple, repeatable security routine is one of the most practical ways to protect online privacy.

 Polish
 English
 Arabic
 French
 Spanish
 Portuguese
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek